DPDP Compliance Implementation Roadmap
A practical roadmap for moving from DPDP requirements to operational readiness — covering scope, data discovery, gap assessment, control design, technical remediation, evidence, validation and ongoing operations.
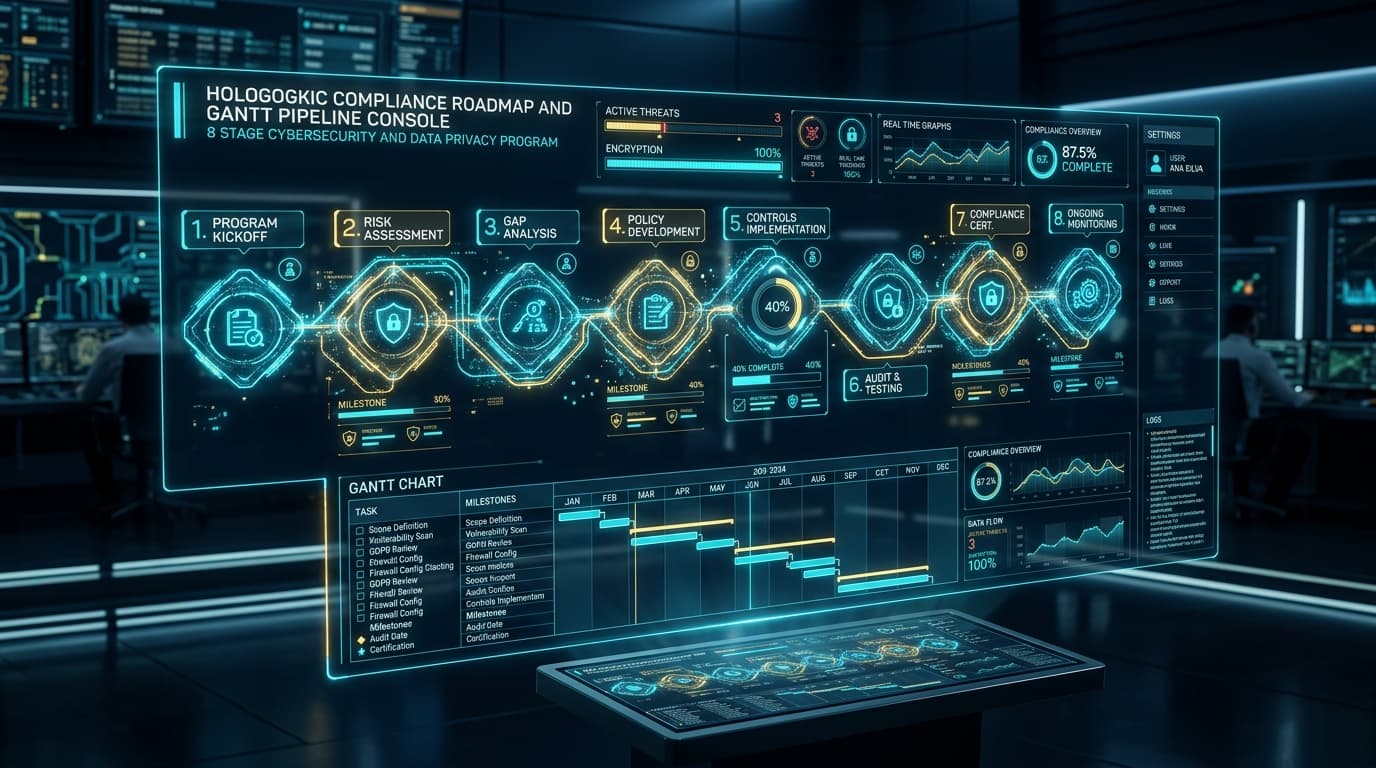
A Practical Roadmap for Moving from DPDP Requirements to Operational Readiness
DPDP implementation is not simply a matter of creating policies, completing a checklist or conducting a one-time assessment. An organisation needs to understand: What applies → what data is processed → where it moves → who is responsible → what controls exist → what needs to change → what depends on what → how implementation will be evidenced → how readiness will be validated. NuageSEC sequences DPDP compliance into an 8-stage operational flow adapted to your processing activities, technology environment, existing controls and applicable requirements under the Digital Personal Data Protection Act, 2023 and the final DPDP Rules, 2025.
Determine applicability, legal entities, business units & boundaries
Inventory personal data, applications, data flows, processors & lifecycle
Evaluate governance, notice, consent, security, access & vendor gaps
Establish target operating model, ownership matrix & dependencies
Execute technical safeguards, IAM, API security & organisational changes
Compile operational proof, system configs, audit logs & agreement records
Test controls, process execution, breach escalation & technical criteria
Embed into product change, vendor onboarding, audits & ongoing operations
What Is a DPDP Compliance Implementation Roadmap?
A DPDP compliance implementation roadmap is a structured plan that converts applicable DPDP requirements into prioritised, sequenced and accountable implementation activities. While a checklist tells you what to examine, a roadmap tells you what to do first, what follows, who owns it, what it depends on, what evidence is required and how to determine whether it is operational.
| Management Question | What the Roadmap Establishes |
|---|---|
| What applies? | Regulatory scope, jurisdictional reach, fiduciary/processor roles and applicable statutory obligations under DPDP Act 2023 and Rules 2025. |
| Where are we today? | Current data inventory, business processes, technology architecture, access paths and baseline control state. |
| What comes first? | Critical dependencies and implementation priorities (P0 to P3) to prevent building on unverified assumptions. |
| What can happen in parallel? | Identified parallel workstreams that do not need to wait for full linear project completion. |
| What proves completion? | Required operational evidence layer, configurations, audit trails and verifiable records. |
| Are we ready? | Measurable readiness criteria, control validation testing and operational verification gates. |
Checklist vs Roadmap: A checklist tells you what to examine. A roadmap tells you what to do first, what follows, who owns it, what it depends on, what evidence is required and how to determine whether it is operational.
SCOPE → DISCOVER → ASSESS → DESIGN → IMPLEMENT → EVIDENCE → VALIDATE → OPERATE
This framework serves as the central implementation model, moving organisations systematically from statutory applicability through to institutionalised operations.
SCOPE — Programme & Regulatory Boundaries
Determine applicability, organisational boundaries, processing roles (Fiduciary vs Processor), legal entities, products, channels, and programme boundaries. Key Deliverable: DPDP Scope & Applicability Statement Readiness Gate: The organisation can explain which activities, entities and processing environments are within the implementation programme.
DISCOVER — Data Environment & Flow Baseline
Understand personal-data processing, systems, flows, access points, processors and lifecycle: Source → Collection → Purpose → Application → Storage → Access → Processor → Transfer → Retention → Disposal. Key Deliverable: Data Processing Inventory + Flow Baseline Readiness Gate: Major processing activities and important data flows have been identified and assigned ownership.
ASSESS — Current-State Gap & Risk Analysis
Identify gaps across governance, notices, consent mechanisms, Data Principal processes, technical safeguards, access controls, processor governance, lifecycle management and incident readiness: Requirement → Current State → Gap → Risk → Owner → Priority → Remediation. Key Deliverable: Prioritised DPDP Gap & Risk Register Readiness Gate: Management can identify the most material gaps and the actions required to address them.
DESIGN — Target Operating Model
Define how DPDP controls will operate inside the organisation, establishing control requirements, responsibilities and cross-functional implementation dependencies. Key Deliverable: DPDP Operating Model + Responsibility Matrix Readiness Gate: Major controls have clear ownership, accountability and escalation paths.
IMPLEMENT — Technical & Organisational Controls
Execute required technical safeguards (IAM, API security, database encryption, cloud posture) and organisational workflows (vendor contracts, employee processes, incident procedures) sequenced by backlog priority. Key Deliverable: Implemented Control Set + Remediation Evidence Readiness Gate: Controls are active in live systems and embedded in daily workflows.
EVIDENCE — The Operational Demonstration Layer
Organise documentation, configurations, access-review logs, processor agreements and system records supporting the implemented controls: Requirement → Control → Owner → Evidence → Review. Key Deliverable: DPDP Evidence Register Readiness Gate: The organisation can demonstrate implementation rather than relying only on written statements.
VALIDATE — Operational & Technical Readiness
Test and review whether implemented controls operate against selected criteria across process execution, technical safeguards, vendor governance, incident escalation and evidence fidelity. Key Deliverable: DPDP Readiness Validation Report Readiness Gate: Controls have undergone technical verification, walkthroughs and tabletop testing.
OPERATE — Ongoing Privacy Management
Embed controls into product changes, vendor onboarding, personal-data incidents, technology architecture updates and ongoing business cycles. Key Deliverable: Ongoing DPDP Operating Programme Readiness Gate: Compliance functions as business-as-usual rather than a static, completed project.
Why DPDP Implementation Should Be Dependency-First
One of the biggest implementation problems is treating every DPDP activity as an independent task. Many controls depend on information or decisions established earlier. Data mapping identifies systems and processors → Systems and processing purposes inform lifecycle and retention decisions → Processor visibility informs vendor governance → Processing environment informs security controls → Implemented controls generate evidence → Evidence supports validation.
Traditional Superficial Approach
- Policy → Checklist → Audit treated as disconnected, isolated tasks
- Drafting privacy notices before knowing which systems process personal data
- Hardening security tools without personal-data flow and repository visibility
- Negotiating vendor DPAs without an accurate sub-processor inventory
- Assuming a checked box on a checklist proves operational compliance
Dependency-First Implementation
- Scope → Data Visibility → Assessment → Control Design → Remediation → Evidence → Validation → Operations
- Baseline data mapping directly informs lifecycle, retention, and storage decisions
- Technical safeguards tailored to verified production databases, APIs, and cloud buckets
- Vendor governance driven by complete data-flow and processor mapping
- Verifiable operational proof generated continuously to substantiate compliance posture
Order of implementation matters: Commencing downstream remediation before establishing baseline data visibility inevitably leads to costly rework, blind spots in vendor pipelines, and unevidenced controls.
Phases 1 to 3: Establishing the Programmatic & Data Baseline
Foundational phases build the empirical foundation required for confident, defensible compliance execution.
Phase 1 — Scope the DPDP Programme
Determine what the organisation actually needs to implement. Identify relevant legal entities, business units, products and services, collection channels, categories of Data Principals, processing activities, Data Fiduciary and Data Processor roles, third-party processing, cross-border flows, and potentially applicable exemptions. Deliverable: DPDP Scope & Applicability Statement Readiness Gate: The organisation can explain which activities, entities and processing environments are within the implementation programme.
Phase 2 — Discover the Data Environment
Establish end-to-end visibility across: Source → Collection → Purpose → Application → Storage → Access → Processor → Transfer → Retention → Disposal. Inventory websites, mobile apps, CRM, HR platforms, databases, cloud accounts, APIs, analytics tools, marketing tech, identity providers, and testing environments. Deliverable: Data Processing Inventory + Data Flow Baseline Readiness Gate: Major processing activities and important data flows have been identified and assigned ownership.
Phase 3 — Assess the Current State
Determine the difference between the organisation's current environment and target state. Assess governance, notices, consent mechanisms, Data Principal processes, technical safeguards, access controls, processor governance, lifecycle management, and incident readiness using: Requirement → Current State → Gap → Risk → Owner → Priority → Remediation. Deliverable: Prioritised DPDP Gap & Risk Register Readiness Gate: Management can identify the most material gaps and the actions required to address them.
Phase 4 — Designing the Target Operating Model
Determining how DPDP controls will operate inside the organisation requires explicit cross-functional alignment. DPDP cannot be isolated to legal or security alone.
| Functional Area | Key Decision & Operating Ownership |
|---|---|
| Governance | Who owns overall programme accountability, board reporting, and executive escalation? |
| Privacy Operations | Who manages day-to-day operational privacy workflows, notices, and Data Principal requests? |
| Security | Who owns technical safeguards, encryption, IAM, vulnerability remediation, and infrastructure protection? |
| Product | How are privacy-by-design requirements incorporated into feature roadmaps, wireframes, and user consent journeys? |
| Engineering | Where and how are privacy controls embedded into CI/CD pipelines, code reviews, schema migrations, and APIs? |
| Vendors & Procurement | How are Data Processors evaluated, contractually bound, audited, and reviewed prior to data sharing? |
| Legal & Regulatory | Who handles statutory interpretation, regulatory liaisons, lawful processing grounds, and contract review? |
| Evidence & Records | Who owns continuous evidence collection, configuration archiving, and repository maintenance? |
| Incident Response | Who coordinates personal-data breach detection, CERT-In/DPBI notifications, and executive response? |
Deliverable: DPDP Operating Model + Responsibility Matrix | Readiness Gate: Major controls have clear ownership, accountability and escalation paths.
Phase 5 — Building the Implementation Backlog
Convert identified gaps into an executable engineering and governance programme. Each activity is tracked with: Owner → Priority → Dependency → Target State → Evidence → Status.
| Priority Tier | Classification | Operational Purpose & Criteria |
|---|---|---|
| P0 — Foundational | Critical Prerequisites | Required before dependent activities can be implemented reliably (e.g. programme scoping, core data inventory, basic IAM). |
| P1 — Material | Core Regulatory Controls | Important regulatory, process, or security gaps with significant compliance exposure (e.g. notice updates, API security, processor DPAs). |
| P2 — Risk Reduction | Defensive Hardening | Improvements that materially strengthen security and privacy posture (e.g. automated retention pruning, MFA enforcement, enhanced audit logging). |
| P3 — Optimisation | Maturity & Efficiency | Automation, self-service portals, privacy workflow orchestration, and long-term governance maturity improvements. |
This prioritisation model allows engineering and privacy teams to distinguish critical dependencies from improvements that can be addressed later in the cycle.
DPDP Implementation Dependency Matrix
This matrix is one of the central decision assets of the roadmap. It answers not just what to do, but what has to happen before something else can be done properly.
| Workstream | Requires First (Prerequisite) | Can Progress Alongside | Required Evidence |
|---|---|---|---|
| Data Mapping | Scope Definition & Legal Boundaries | Governance Setup & Charter | Data Processing Inventory / Data Flow Maps |
| Gap Assessment | Initial Data Flow Baseline | Governance & Policy Review | Prioritised Gap & Risk Register |
| Security Assessment | Relevant Systems & Personal-Data Scope | Gap Assessment Analysis | VAPT & Security Assessment Findings |
| Processor Governance | Processor & Sub-Processor Visibility | Security Remediation | Processor Register, DPAs & Review Logs |
| Rights Processes | Data Location & Process Visibility | Vendor Remediation | Workflow Runbooks & Simulated Request Records |
| Lifecycle Controls | Data Inventory + Processing Purpose Context | Other Control Design | Automated Retention Scripts & Disposal Certificates |
| Incident Readiness | System Scope & Logging Capabilities | Security Remediation | Incident Playbooks & Tabletop Exercise Evidence |
| Evidence Framework | Target Control Design & Ownership | Active Implementation | Centralised DPDP Evidence Register |
| Validation | Implemented Technical & Process Controls | Final Remediation Fixes | DPDP Readiness Validation Report |
Crucial Insight: Attempting to implement Rights Processes or Lifecycle Controls before Data Mapping produces brittle workflows that fail during audits.
Phase 6 — Implementing Technical and Organisational Safeguards
The final DPDP Rules explicitly mandate reasonable security safeguards to protect digital personal data. Implementation must span both procedural governance and deep engineering safeguards.
Organisational Controls
- Documented internal operating procedures and privacy workflow runbooks
- Role-based governance, executive reporting, and designated privacy owners
- Vendor and Data Processor onboarding, due diligence, and contract schedules
- Workforce data handling policies, clean desk standards, and confidentiality deeds
- Incident escalation matrices, communication trees, and statutory notification playbooks
- Formal evidence collection ownership and regular management review cycles
Technical Safeguards
- Identity & Access Management (IAM), Least Privilege, and Privileged Access Management (PAM)
- Application & API security testing, payload validation, and OWASP Top 10 hardening
- Cloud security posture management, container isolation, and secure bucket configurations
- Database access controls, role segregation, and field-level encryption/masking where appropriate
- Centralised audit logging, SIEM/MDR monitoring, and immutable tamper-resistant trails
- Automated data lifecycle enforcement, archival scheduling, and secure cryptographic deletion
The final DPDP Rules identify reasonable security safeguards including encryption/obfuscation/masking/virtual tokens where appropriate, access controls, logging, backups and continuity. They do not prescribe one universal technology stack for every organisation. Deliverable: Implemented Control Set + Remediation Evidence.
Phase 7 — Building the Evidence Layer & 5 Maturity Stages
A mature implementation programme should not end with: 'The policy exists.' The stronger question is: 'Can the organisation demonstrate that the control has actually been implemented?' Every control must advance through five distinct maturity stages.
Stage 1 — Defined
The requirement and target control standard are formally documented, approved, and integrated into internal policy frameworks.
Stage 2 — Assigned
A specific role, engineering team, or business lead is formally designated as accountable for the operation and maintenance of the control.
Stage 3 — Implemented
The control exists and functions within the relevant operational workflow, production application, API, or cloud infrastructure.
Stage 4 — Evidenced
The organisation continuously captures verifiable, timestamped operational proof (system configs, access audit logs, signed DPAs, review tickets).
Stage 5 — Validated
The control has been independently tested, reviewed, or challenged through assessment or simulation against defined criteria.
Deliverable: DPDP Evidence Register | Readiness Gate: The organisation can demonstrate implementation rather than relying only on written statements.
Phase 8 — Validating Operational Readiness
Readiness validation determines whether implemented controls and processes work as intended against selected criteria across 5 operational dimensions.
Statutory Breach Clarification: Rule 7 provides for notification to affected Data Principals without delay and information to the Data Protection Board of India without delay, while Rule 7(2)(b) provides for detailed information to the Board within 72 hours of becoming aware of a personal-data breach (unless a longer period is permitted by the Board on written request). Therefore, DPDP should not be characterized as having a blanket '72-hour breach notification grace period'. Deliverable: DPDP Readiness Validation Report. Explore DPDP Data Breach & Incident Readiness → →
Phase 9 — Moving from Project to Operations
DPDP implementation should eventually become part of normal business processes. The goal is to prevent DPDP compliance from becoming a project that is 'completed' and then forgotten.
New Product or Feature
Trigger automated privacy and control review before architectural sign-off and deployment.
New Vendor Onboarding
Execute Data Processor due diligence, technical assessment, and contractual DPA binding before granting data access.
New Processing Purpose
Evaluate statutory lawful grounds (consent vs specified legitimate uses) and update notices accordingly.
New Infrastructure or Database
Conduct personal-data flow and repository mapping before connecting to production networks.
Major Technology Change
Mandate technical application and API security VAPT to prevent regression in technical safeguards.
Personal-Data Incident
Execute rapid response, root-cause investigation, statutory board notification, and remediation evidence review.
Deliverable: Ongoing DPDP Operating Programme | Readiness Gate: Controls function as business-as-usual across all operational units.
What Can Run in Parallel?
A mature programme is not entirely linear. Once scope and baseline visibility are sufficiently established, several workstreams can progress simultaneously without violating core dependencies.
A Practical 90-Day Starting Sequence
This is an illustrative project sequence, not a statutory deadline. It provides engineering and privacy teams with clear 30-day decision gates.
Focus: Applicability and scope, programme owners, major processing activities, important systems, processor visibility, initial gaps, critical security issues. Decision Gate: Do we have enough visibility to plan remediation confidently?
Focus: Prioritising material gaps, defining control owners, establishing dependencies, designing key workflows, prioritising processor remediation, defining evidence requirements, preparing technical remediation plans. Decision Gate: Do we have an agreed implementation backlog with owners, dependencies and evidence requirements?
Focus: High-priority technical remediation, priority process implementation, processor remediation, evidence collection, process testing, incident-readiness exercises, residual-risk tracking. Decision Gate: Are priority controls moving from documentation into actual operation?
DPDP Regulatory Timeline & Implementation Reality
The final DPDP Rules were notified on 13 November 2025. Their commencement is phased. Rules 1, 2 and 17–21 commenced on publication; Rule 4 is scheduled one year after publication; and Rules 3, 5–16, 22 and 23 are scheduled eighteen months after publication. The Act also has a phased commencement notification.
| Statutory Date | Regulatory Provision | Implementation Planning Significance |
|---|---|---|
| 13 November 2025 | Rules 1, 2, 17–21 Commenced | Initial specified provisions and procedural Rules became operative upon official notification. |
| 13 November 2026 | Rule 4 Scheduled to Commence | Detailed notice requirements under Section 5 become operative (1-year milestone). |
| 13 May 2027 | Substantive Act Provisions & Rules | Large group of substantive Act provisions and Rules 3, 5–16, 22, and 23 scheduled to commence (18-month milestone). |
| Ongoing Operations | Continuous Compliance Lifecycle | Controls, evidence registers, processor reviews, and operating processes require continuing management. |
Important distinction: Commencement date ≠ implementation project duration. A business may need substantial lead time for data mapping, engineering changes, processor remediation, workflow development, security remediation and testing.
Where Significant Data Fiduciary (SDF) Requirements Fit
SDF requirements should be treated as a conditional workstream, not a universal requirement for every organisation. The Act provides for Central Government designation of Significant Data Fiduciaries based on volume, sensitivity, national security, and risk to Data Principals.
SDF Applicability Assessment
Assess whether processing scale, sensitivity, or sector classification triggers SDF designation under Section 10.
Additional Statutory Mandates
If designated: identify additional statutory mandates including independent Data Audits, DPIA frameworks, and a resident Data Protection Officer (DPO).
Dedicated SDF Implementation
Incorporate DPIA triggers into CI/CD and product design, configure algorithmic risk reviews, and establish DPO escalation channels.
Periodic Audit & Board Reporting
Establish recurring audit protocols under Rule 13 (scheduled in the 18-month group) with independent assurance reporting.
Structure: SDF Applicability Assessment → Additional Requirements → Dedicated Implementation → Validation, rather than assuming every organisation needs an identical SDF programme.
DPDP Readiness Gates: Measuring Programme Maturity
Use these six gates to measure programme maturity. The objective is not simply 'we completed the DPDP project', but 'we can demonstrate that relevant controls are operating.'
Gate 1 — Scope Ready
Applicability, legal entities, products, cross-border flows, and programme boundaries are formally documented and approved.
Gate 2 — Data Ready
Major processing activities, systems, repositories, APIs, and third-party processors are identified and assigned ownership.
Gate 3 — Assessment Ready
Prioritised gap and risk registers are complete across technical, governance, and vendor domains.
Gate 4 — Implementation Ready
Control owners, engineering backlogs, dependencies, and remediation milestones (P0–P3) are assigned and approved.
Gate 5 — Evidence Ready
Centralised evidence register is active, linking system configs, access audit logs, and DPAs to each implemented control.
Gate 6 — Operationally Ready
Controls function within normal business processes, product changes, vendor onboarding, and incident response.
Common DPDP Implementation Mistakes to Avoid
Organisations frequently derail compliance programmes by treating DPDP as a legal drafting exercise rather than an operational engineering transformation.
Starting with Documentation First
Drafting lengthy privacy notices and policies in a silo before understanding actual data flows and technical architecture.
Lead with Data Visibility
Map production databases, APIs, and applications first so policies accurately reflect real-world data practices.
Treating the Checklist as Implementation
Ticking off checklist boxes in a spreadsheet and assuming compliance has been achieved.
Demand Verifiable Operational Evidence
Verify that controls exist within live systems, are enforced via IAM/code, and produce auditable proof.
Ignoring Third-Party Data Processors
Focusing solely on internal databases while neglecting SaaS vendors, cloud partners, and sub-processors.
Establish End-to-End Vendor Governance
Enforce processor inventories, contractual DPAs, security reviews, and breach notification obligations.
Separating Privacy and Security Completely
Leaving legal to handle DPDP while security teams work in isolation on standard IT tasks.
Integrate Privacy Engineering with VAPT
Align DPDP requirements with application security, API testing, encryption, and privileged access safeguards.
Implementing Without an Evidence Model
Building controls but failing to document configurations, audit trails, or operational logs.
Maintain a Continuous Evidence Register
Ensure every implemented safeguard has an assigned owner, timestamped proof, and periodic review records.
Waiting Until the Final Commencement Date
Delaying programme kickoff until May 2027 when substantive provisions commence.
Start Foundational Scoping Now
Allow necessary lead time for data discovery, engineering refactoring, vendor renegotiation, and validation.
DPDP Implementation Deliverables
A structured DPDP implementation programme produces eight tangible, audit-ready operational artifacts.
Applicability & Scope Statement
Defines the programme boundaries, legal entities, products, and statutory roles.
Data Processing Baseline
Documents relevant processing activities, repositories, flows, and lifecycles.
Gap & Risk Register
Prioritises control, process, and technical security gaps by business impact.
Control & Responsibility Matrix
Maps DPDP controls to specific cross-functional owners and escalation paths.
Implementation Backlog
Sequences remediation according to P0–P3 priorities and critical dependencies.
Technical & Organisational Remediation Plan
Translates statutory requirements into concrete engineering and procedural actions.
Evidence Register
Defines and organises the proof required for every implemented safeguard.
Readiness Validation Report
Documents implementation status, validation results, and residual risk tracking.
DPDP Checklist vs Gap Assessment vs Audit vs Roadmap
This distinction clarifies the role of each instrument in the NuageSEC compliance cluster, keeping each service separate and purposeful.
| Compliance Asset / Instrument | Primary Question It Answers |
|---|---|
| Checklist | What should we review? (Broad self-assessment overview of statutory questions). |
| Gap Assessment | What is missing or incomplete? (Evaluates current state against statutory baseline). |
| Security Assessment | What technical weaknesses need attention? (VAPT and cloud security testing). |
| Audit | Have defined controls been implemented and supported by sufficient evidence against selected criteria? |
| Implementation Roadmap | What should happen first, what depends on it and how do we reach operational readiness? |
| Implementation Service | Who can help execute the required technical, procedural, and vendor changes? |
Which DPDP Service Should You Use Next?
Select your current operational situation to navigate to the appropriate next step in the compliance journey.
Frequently Asked Questions About DPDP Implementation
What is a DPDP compliance implementation roadmap?
It is a structured plan that translates applicable DPDP requirements into sequenced implementation activities, owners, dependencies, evidence requirements and readiness milestones.
What should an organisation do first for DPDP implementation?
Begin by establishing applicability and scope, followed by sufficient visibility into personal-data processing. Downstream remediation decisions become more reliable when the organisation understands its actual processing environment.
Is a DPDP implementation roadmap the same as a gap assessment?
No. A gap assessment identifies missing or incomplete areas. The roadmap determines how those gaps should be sequenced and addressed.
Does every organisation need a DPDP audit?
No universal annual audit requirement applies to every organisation. Additional audit obligations apply in the SDF context under the statutory framework.
Does DPDP require consent for every processing activity?
No. The Act provides for consent as well as specified legitimate uses. The implementation programme should therefore assess the applicable basis for each processing activity rather than assume everything is consent-based.
Does DPDP require all personal data to remain in India?
The Act does not establish a blanket India-only storage requirement for every organisation. Section 16 provides a framework concerning processing of personal data outside India and restrictions that may be notified by the Central Government.
Is a privacy policy enough for DPDP implementation?
No. Implementation involves the organisation's data environment, processes, technical and organisational safeguards, third parties, evidence and operational ownership.
How long does DPDP implementation take?
There is no single period that applies to every organisation. The appropriate timeline depends on the complexity of the organisation's data-processing environment, technology, vendors, existing controls and remediation requirements.
Build Your DPDP Compliance Implementation Roadmap
Know what applies. Know what comes first. Build what can be evidenced. NuageSEC can help organisations translate DPDP requirements into a structured implementation programme aligned with their data environment, cybersecurity controls, dependencies and remediation priorities.
Instant access · XLSX + PDF formats · Includes 2026-27 phased enforcement roadmap
Start Your DPDP Assessment
Tell us about your organization. Our DPDP team will get back within one business day to define the right scope and next steps.
